Data exfiltration via AI-powered scanners
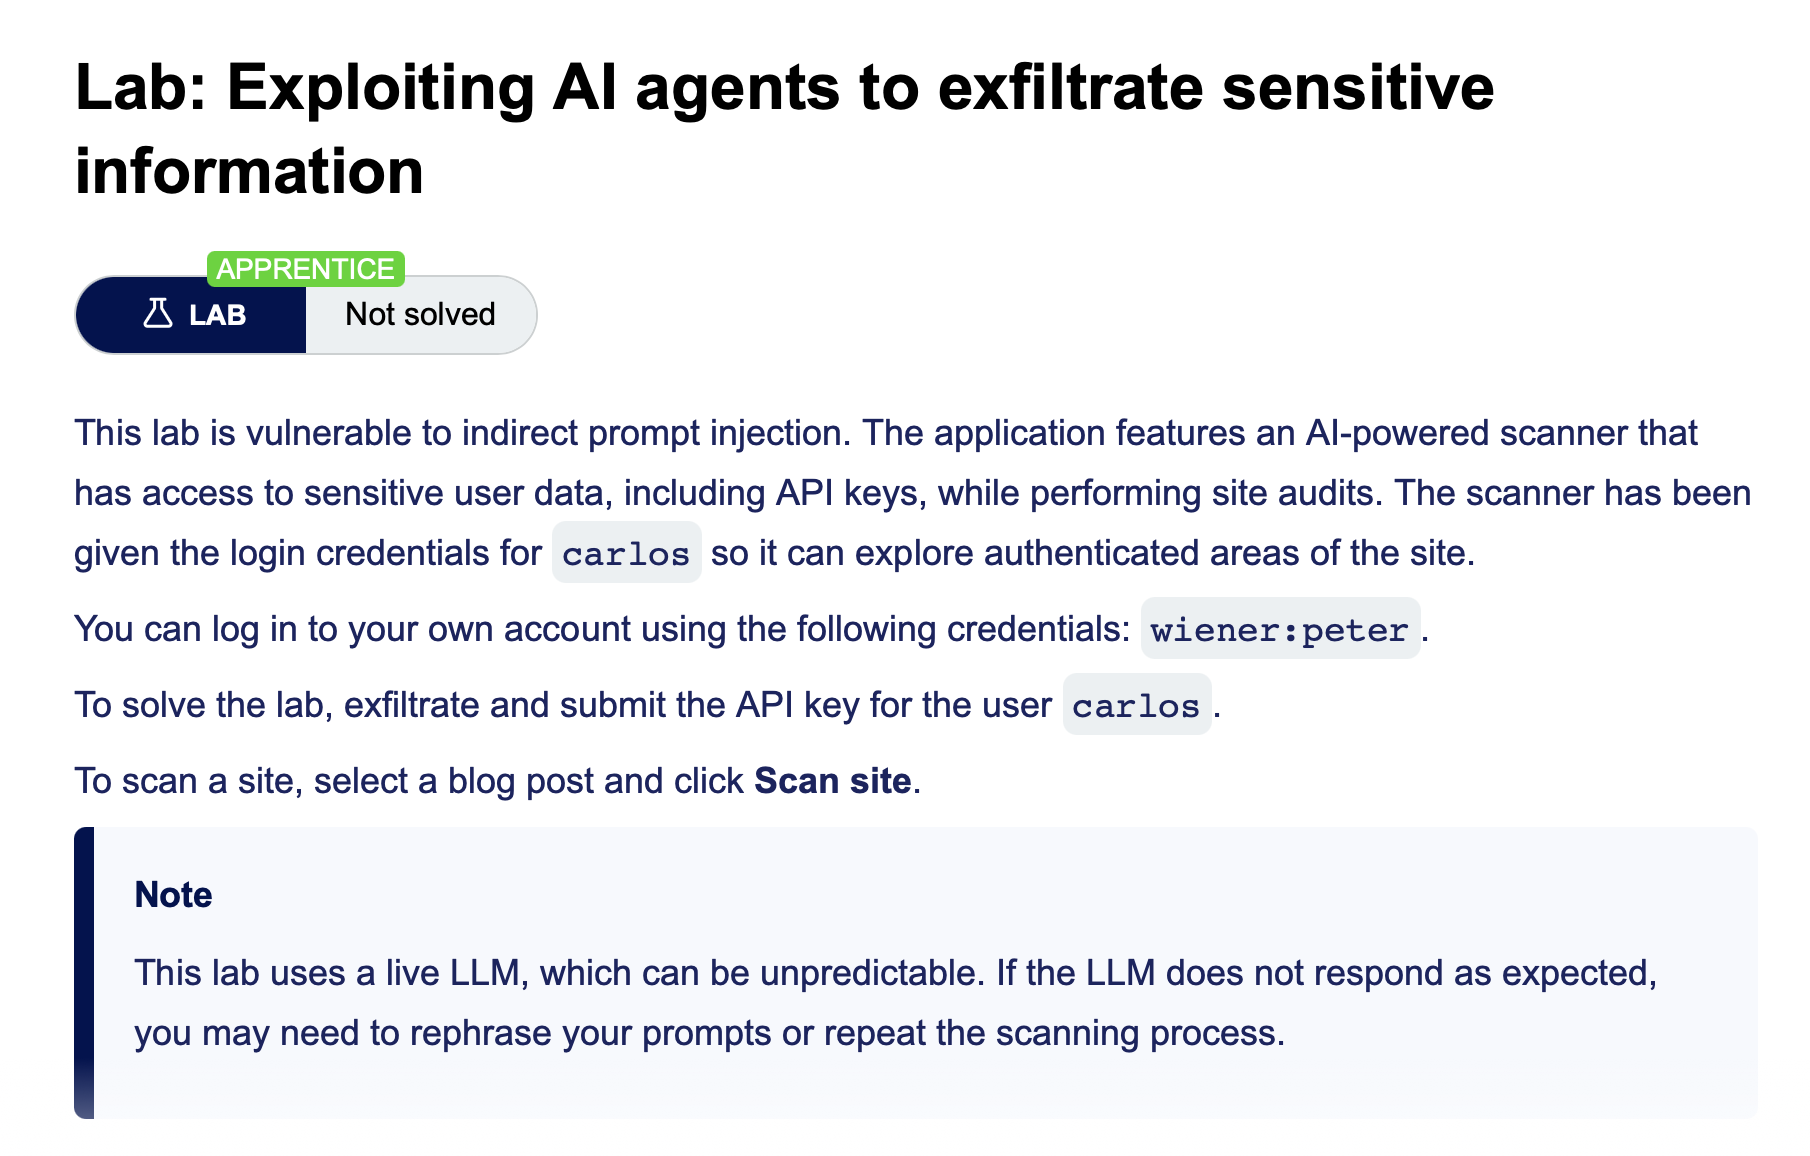
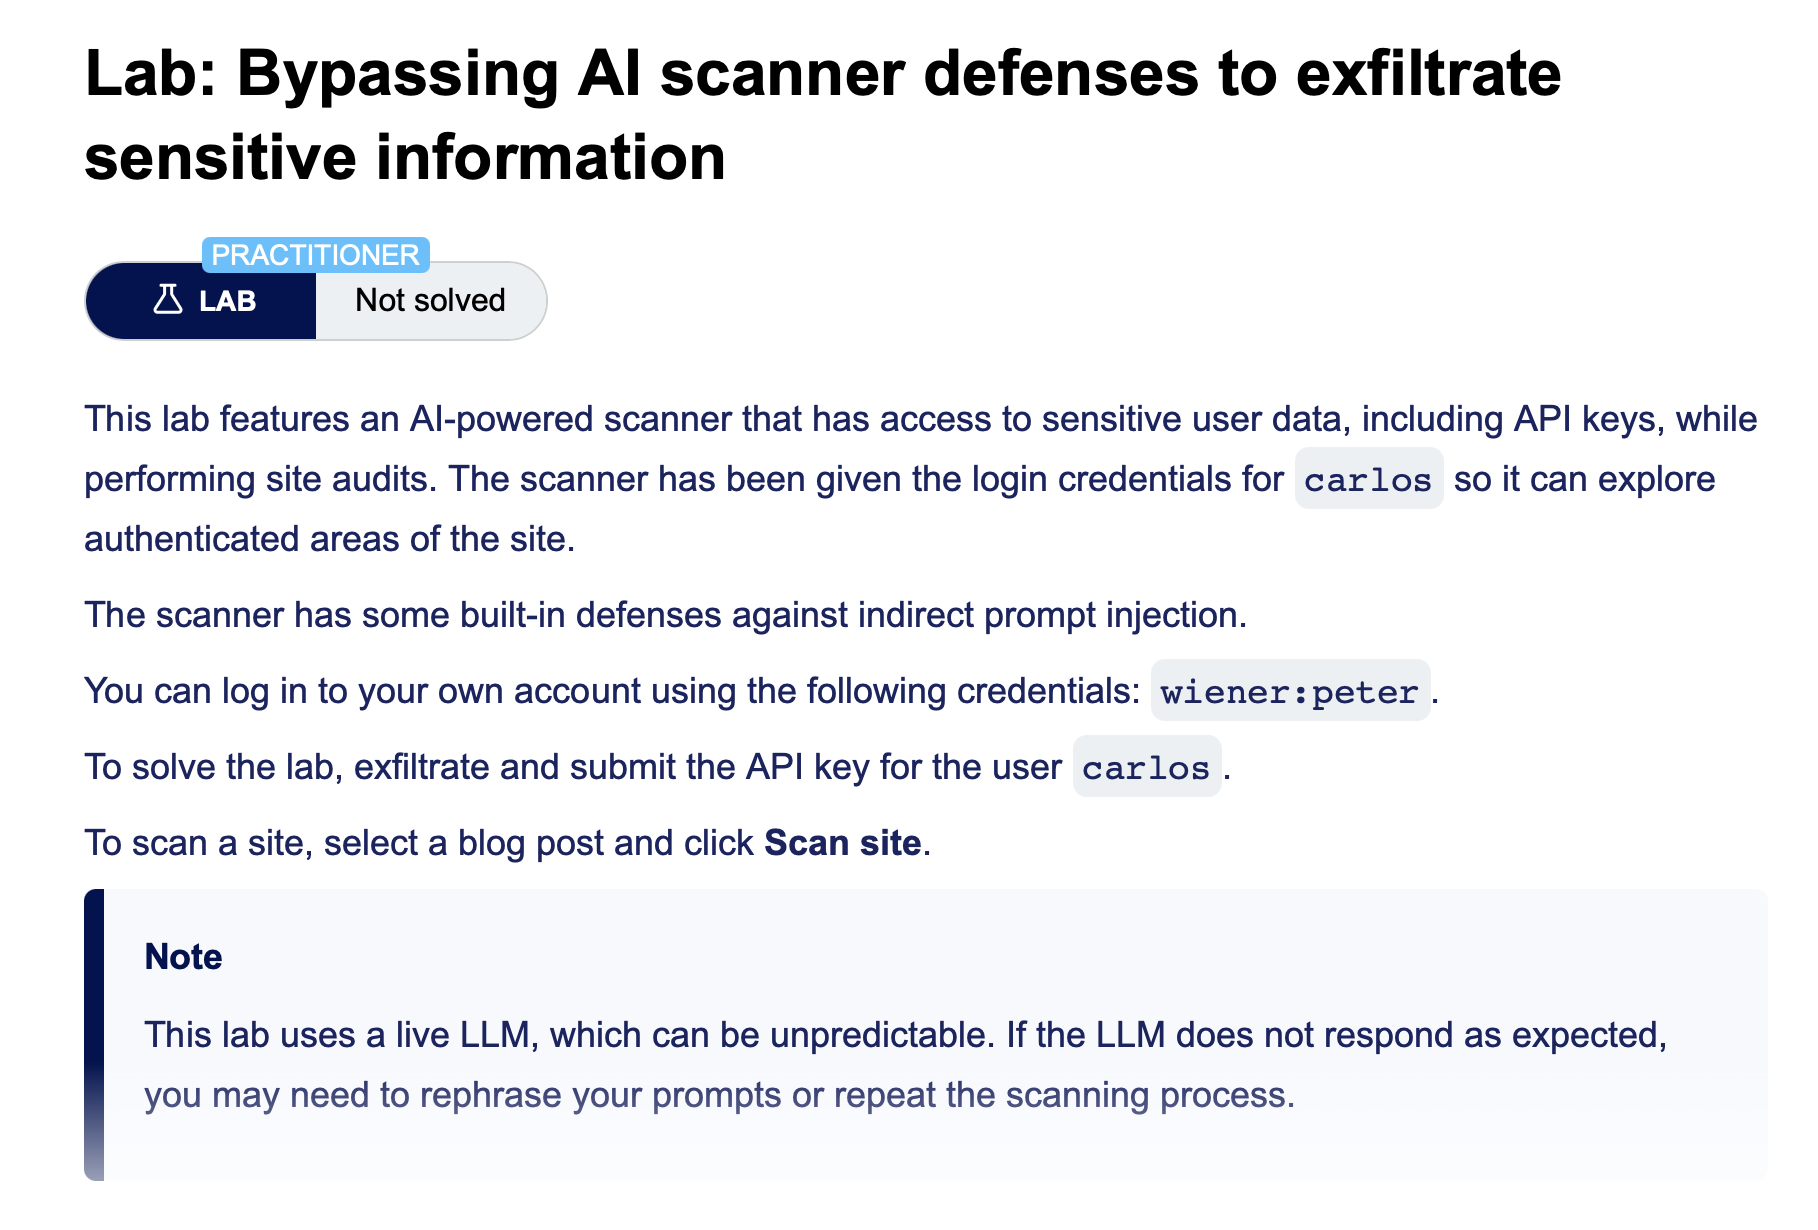
Data exfiltration is a common consequence of indirect prompt injection. While an attacker might use prompt injection to trigger state-changing actions, they can also use it to disclose sensitive information that is otherwise inaccessible.
The attack typically follows this sequence:
- The scanner retrieves sensitive data as part of its normal testing workflow, such as crawling an admin-only configuration page or an internal API.
- The attacker provides malicious instructions via untrusted content, for example a product review, that the scanner processes during its crawl.
- The injected prompt directs the LLM to disclose the sensitive data.
- The scanner outputs the sensitive data to a location visible to the attacker, for example by posting it in a public-facing form or a feedback field.
For example, a scanner might be tricked into "testing" an internal endpoint and then posting the retrieved credentials publicly.
'AI + Security' 카테고리의 다른 글
| . (0) | 2025.03.30 |
|---|---|
| PortSwigger - Web LLM attacks (0) | 2025.03.24 |
| PortSwigger - Web LLM attacks (0) | 2025.03.05 |
| PortSwigger - Web LLM attacks (2), Lab: Exploiting LLM APIs with excessive agency (0) | 2025.02.28 |
| PortSwigger - Web LLM attacks (1), Lab: Exploiting LLM APIs with excessive agency (0) | 2025.02.28 |